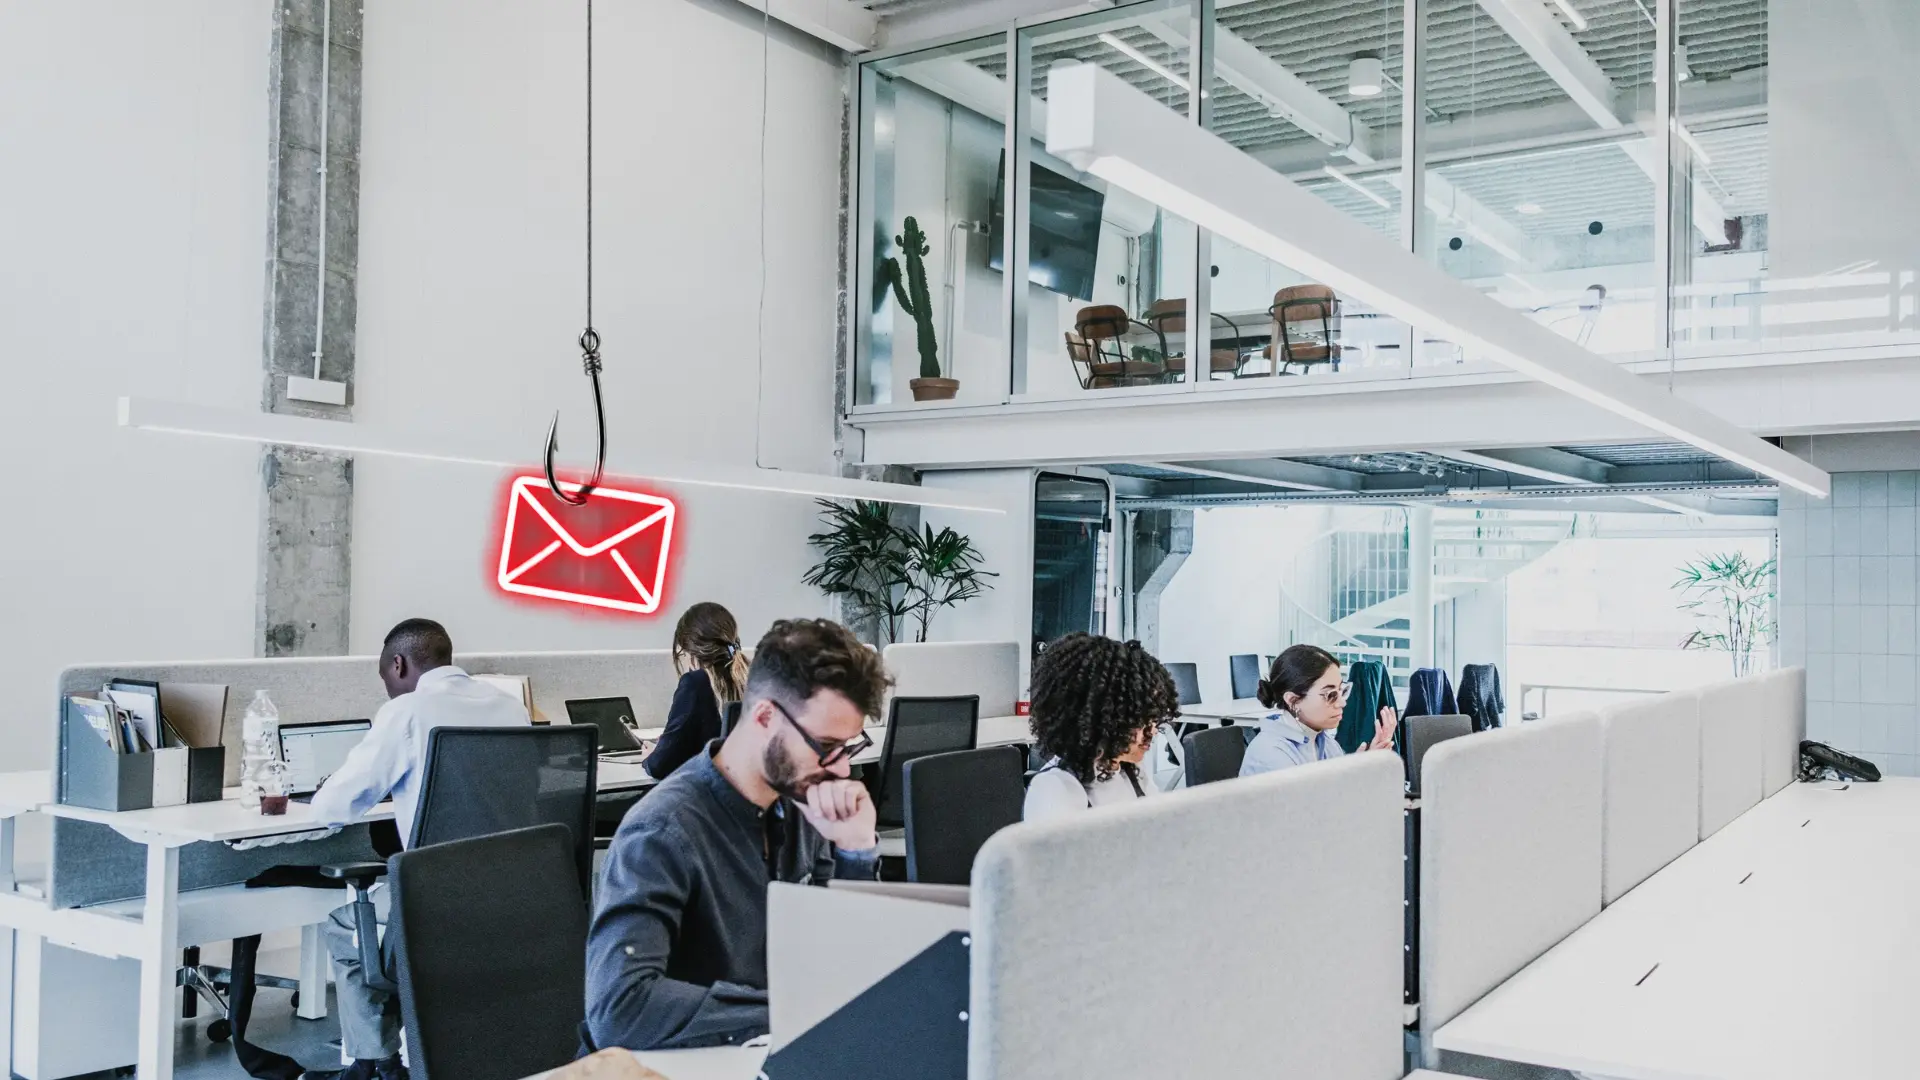
Picture this. It's a busy Tuesday morning. Your office manager, one of the most trusted people on your team, gets an email that looks like it's from your bank. She clicks the link, enters her login, and goes back to work.
Nobody broke in. Nobody hacked a firewall. And yet, by Friday, someone in another country has access to your email, your client files, and possibly your bank account.
She didn't mean to do anything wrong. That's exactly the problem.
What many business owners miss
When most small business owners think about an "inside threat," they picture a disgruntled employee stealing files on the way out the door. That does happen. But it's not the inside threat most likely to hurt you.
The bigger risk is the good employee who makes an honest mistake. The person who reuses a password, saves client data to a personal Dropbox, or approves a fake invoice because the email looked real. These are unintentional inside threats, and they're behind far more security incidents than malicious insiders.
The good news? Unlike a rogue employee, accidental mistakes are very preventable once you know where to look.
What is an unintentional inside threat?
An unintentional inside threat is a security risk caused by someone inside your business, like an employee, contractor, or vendor, who exposes data or systems by accident. There's no bad intent. It's usually a rushed click, a shortcut, or simply not knowing better.
Common examples include:
- Clicking a phishing link or opening a fake attachment
- Reusing the same password across work and personal accounts
- Emailing sensitive files to the wrong person
- Saving company data to personal devices or unapproved cloud apps
- Leaving a laptop unlocked in a coffee shop or car
- Approving a wire transfer or gift card request from a spoofed "boss" email
- Pasting client information into free AI tools without thinking about where that data goes
Intentional vs. unintentional inside threats: what's the difference?
The difference comes down to motive. An intentional insider sets out to cause harm. An unintentional insider causes harm while trying to do their job.
Intentional inside threats
- Who it is: A disgruntled, departing, or financially motivated employee or contractor
- Motive: Revenge, profit, or helping a competitor
- Typical actions: Stealing client lists, deleting data, selling logins
- How often it happens: Less common
- Warning signs: Behavior changes, unusual downloads, access after hours
- Best defense: Access controls, monitoring, and clean offboarding
Unintentional inside threats
- Who it is: A well-meaning employee, contractor, or vendor
- Motive: None. It's a mistake or a shortcut
- Typical actions: Clicking phishing links, using weak passwords, sending emails to the wrong person
- How often it happens: Far more common
- Warning signs: Often none until something goes wrong
- Best defense: Training, simple processes, and technical safety nets
Here's the key takeaway for small businesses: you can't train away bad intent, but you can absolutely reduce honest mistakes. That's why unintentional threats are where most owners get the biggest return on their security effort.
Why so many business owners don't see it coming
If accidental insider threats are so common, why do they fly under the radar? A few reasons come up again and again.
"I trust my people." You should. But trust and security aren't the same thing. Your best employee can still fall for a well-crafted scam, especially on a busy day.
"We're too small to be a target." Cybercriminals love small businesses because they usually have fewer defenses. Most attacks are automated, so criminals aren't picking you by name. They're casting a wide net and waiting for someone to click.
"Our IT is handled." Antivirus and a firewall are important, but they can't stop someone from typing their password into a fake login page. Technology covers part of the risk. People cover the rest.
Mistakes don't look like attacks. A misdirected email or a reused password doesn't set off alarms. Often, the first sign of trouble is a client calling to ask why they got a strange invoice from you.
Nobody wants to admit it. Employees who make a mistake may stay quiet out of embarrassment or fear. The longer a problem goes unreported, the more damage it can do.
8 ways to reduce unintentional inside threats
You don't need a huge budget to make a real difference. Start with these.
- Make security training ongoing, not once a year. Short, regular lessons and simulated phishing emails keep security top of mind. A 10-minute refresher every month beats a two-hour session nobody remembers.
- Turn on multi-factor authentication (MFA) everywhere. If a password gets stolen, MFA is often the thing that stops the criminal from getting in. Prioritize email, banking, and remote access.
- Give people a password manager. It removes the temptation to reuse passwords or write them on sticky notes.
- Limit access to what each person needs. Not everyone needs access to payroll or every client folder. Fewer keys means fewer doors left open by mistake.
- Create a "verify before you pay" rule. Any request to change bank details, send a wire, or buy gift cards gets confirmed by phone, using a number you already have on file.
- Set clear rules for personal devices, cloud apps, and AI tools. Spell out which apps are approved and what data should never be pasted into a free AI tool or personal account.
- Make it safe to report mistakes. Tell your team: if you clicked something weird, tell us right away and you won't get in trouble. Fast reporting can turn a disaster into a minor hiccup.
- Back up your data and test the backups. When a mistake does slip through, good backups mean you can recover quickly instead of starting from scratch.
Not sure where your gaps are? Let's find out together.
Most business owners we talk to have at least one blind spot they didn't know about, whether it's an old account that never got shut off, a team that hasn't had security training, or a payment process that relies on email alone.
At Stimulus Technologies, we've been helping small and mid-sized businesses stay secure since 1995. In a free 15-minute consult, we'll talk through how your team works, point out the most likely risks, and give you a few practical next steps. No pressure and no tech jargon.
Book your free 15-minute consult today and find out where your business stands before a simple mistake becomes an expensive one.
Frequently asked questions
What is an unintentional insider threat?
It's a security risk caused by an employee, contractor, or vendor who accidentally exposes company data or systems. Common causes include phishing clicks, weak or reused passwords, and sending sensitive information to the wrong person.
What's the difference between an intentional and unintentional insider threat?
Intent. An intentional insider deliberately causes harm, often for revenge or money. An unintentional insider causes harm by mistake while trying to do their job.
Which type of insider threat is more common?
Unintentional insider threats are far more common. Human error, like clicking a malicious link or misdirecting an email, plays a role in a large share of data breaches.
Can a small business really be targeted by cybercriminals?
Yes. Small businesses are frequent targets because they often have fewer security protections. Most attacks are automated and aimed at anyone who will click, regardless of company size.
How can I prevent employees from making security mistakes?
Combine regular security awareness training with simple safeguards: multi-factor authentication, a password manager, limited access to sensitive data, a phone verification rule for payments, and a culture where people feel safe reporting mistakes.
Is security awareness training worth it for a small team?
Yes. Short, ongoing training is one of the most cost-effective ways to reduce risk, because it targets the most common cause of incidents: everyday human error.
What should an employee do if they think they clicked a bad link?
Report it right away to your IT provider or manager. Disconnect from the network if instructed, and change any passwords that may have been entered. Speed matters more than blame.
Schedule your free 15-minute IT consult now.